Directory-backed selection
Choose protected people from a searchable Entra user picker instead of maintaining fragile free-text account identifiers.
Emergency access monitoring
Select emergency-access identities directly from your Entra directory and give any captured change involving those protected accounts immediate, critical visibility.
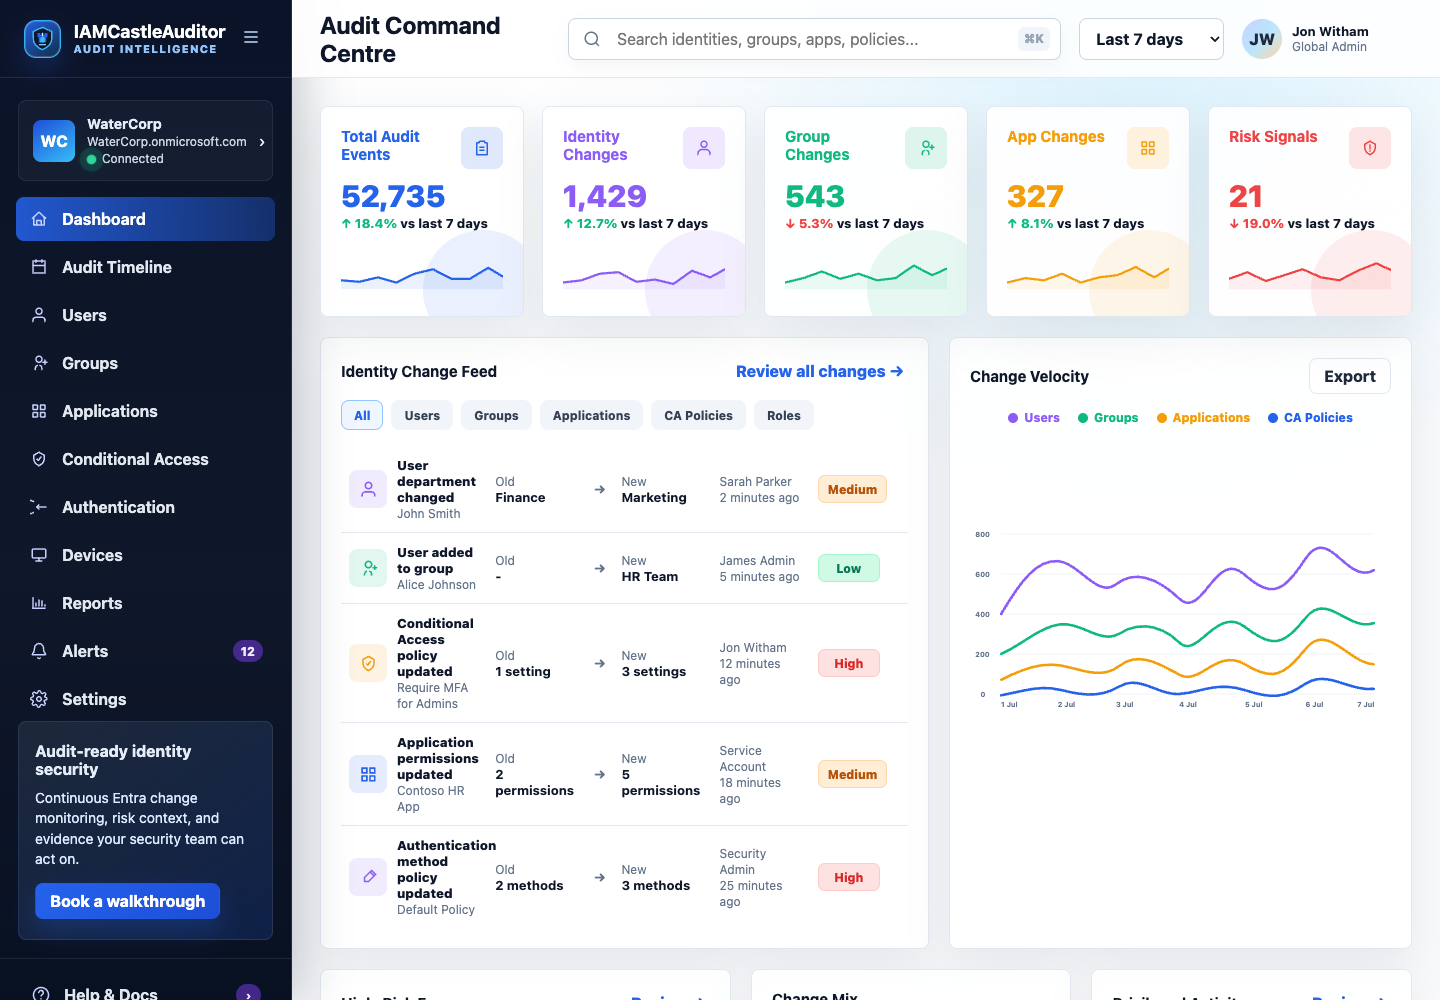
Choose protected people from a searchable Entra user picker instead of maintaining fragile free-text account identifiers.
Promote evidence involving a protected emergency-access identity to critical so it cannot blend into routine directory activity.
Send connector and configured security notifications to active customer administrators plus an optional security operations mailbox.
Emergency-access accounts exist for the moment ordinary authentication or administration paths are unavailable. Because they are intentionally powerful and rarely used, unexpected changes to their identity attributes or surrounding access configuration deserve special attention.
IAMCastle lets an administrator select current Entra users as protected break-glass identities. The selection is stored for the customer and matched against incoming evidence so relevant changes receive critical treatment in the product.
This capability complements, rather than replaces, Microsoft's recommendations for emergency-access account design, authentication methods, monitoring, and periodic validation. IAMCastle remains read only and does not manage the account itself.