One searchable audit record
Review changes across users, groups, devices, applications, roles, Conditional Access policies, and tenant configuration without moving between separate Microsoft portals.
Microsoft Entra ID auditing
IAMCastle continuously collects read-only Microsoft Entra ID evidence and turns technical directory activity into a clear record of who changed what, when it happened, and the values before and after.
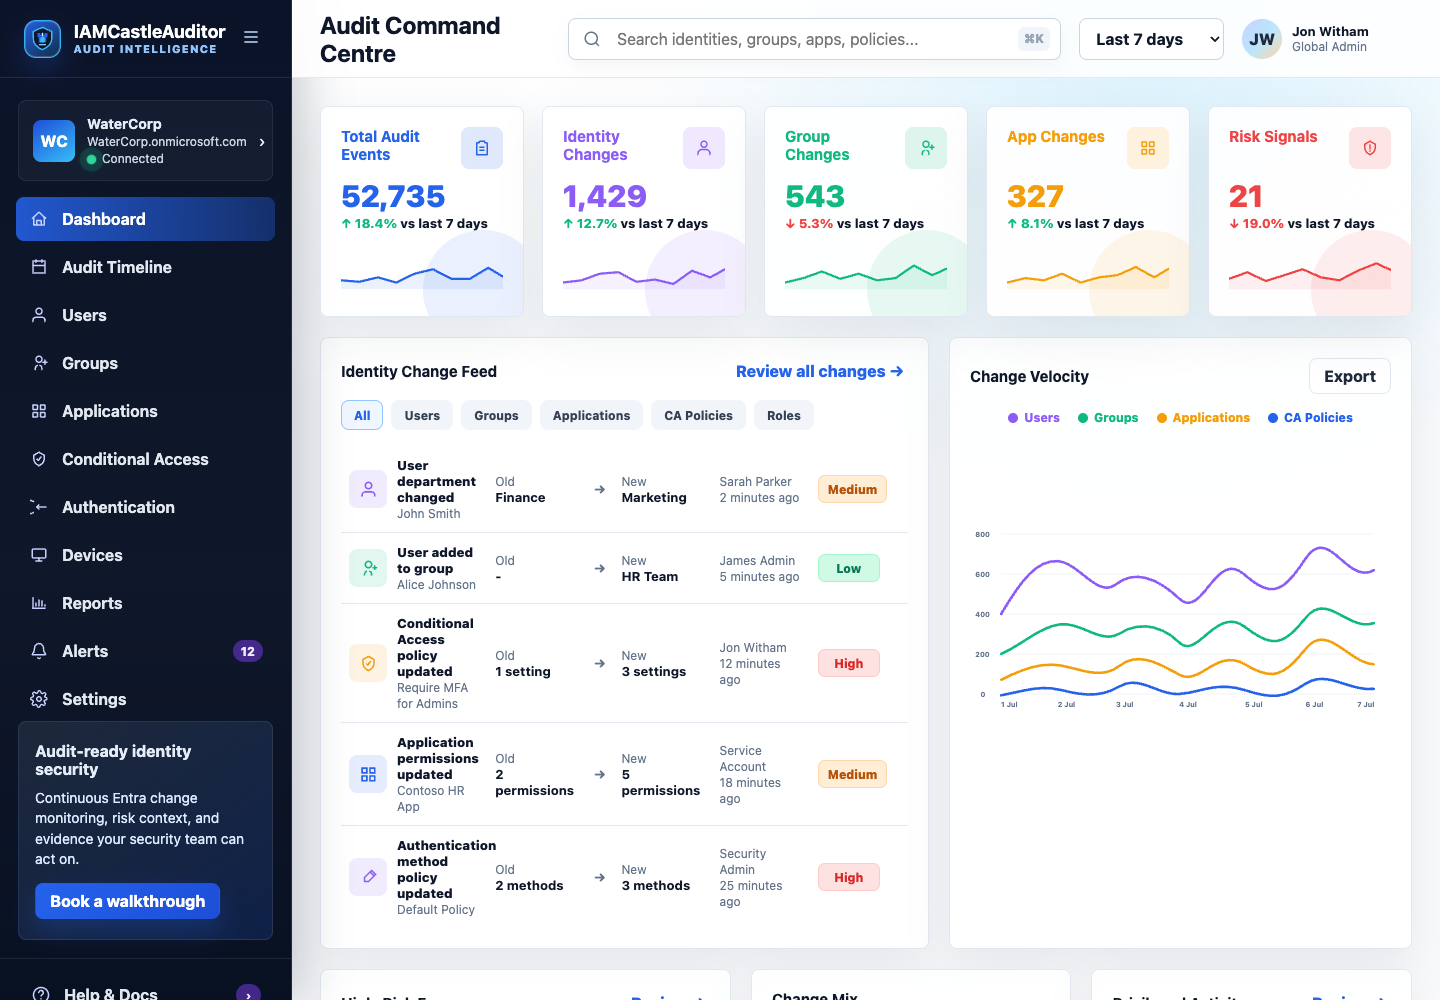
Review changes across users, groups, devices, applications, roles, Conditional Access policies, and tenant configuration without moving between separate Microsoft portals.
Resolve Entra object identifiers into useful names and present old and new values in plain English so investigations do not begin with raw GUIDs or Graph payloads.
Keep searchable evidence in an IAMCastle-controlled store with tenant-specific SHA-256 hash chaining to make later alteration or missing records detectable.
Microsoft Entra ID is constantly changing as administrators, applications, automation, and governance processes update identities and access. Native logs are valuable, but investigations often require context that is spread across object types or no longer present in the current directory state.
IAMCastle combines Microsoft directory audit events with independent object snapshots. That local history provides the comparison point needed to show previous and current values, while scheduled collection assurance makes a stopped connector visible rather than silently creating an evidence gap.
The service is entirely cloud based. Customers connect their own tenant through Microsoft admin consent, authenticate using Microsoft SSO, and grant only the read-only Microsoft Graph permissions required for collection.